SEBI CSCRF · CERT-In Direction 70B/2022 · DPDP Act 2023
Compliance evidence your auditor can verify.
Sanad turns your day-to-day compliance work — incident reports, consent records, policies, endpoint logs — into signed, tamper-evident evidence, collected automatically from your own machines and ready for any SEBI, CERT-In or DPDP review.
DPIIT-recognised startup · Govt of Haryana Category-1 funded · Compliance data stored and processed in India
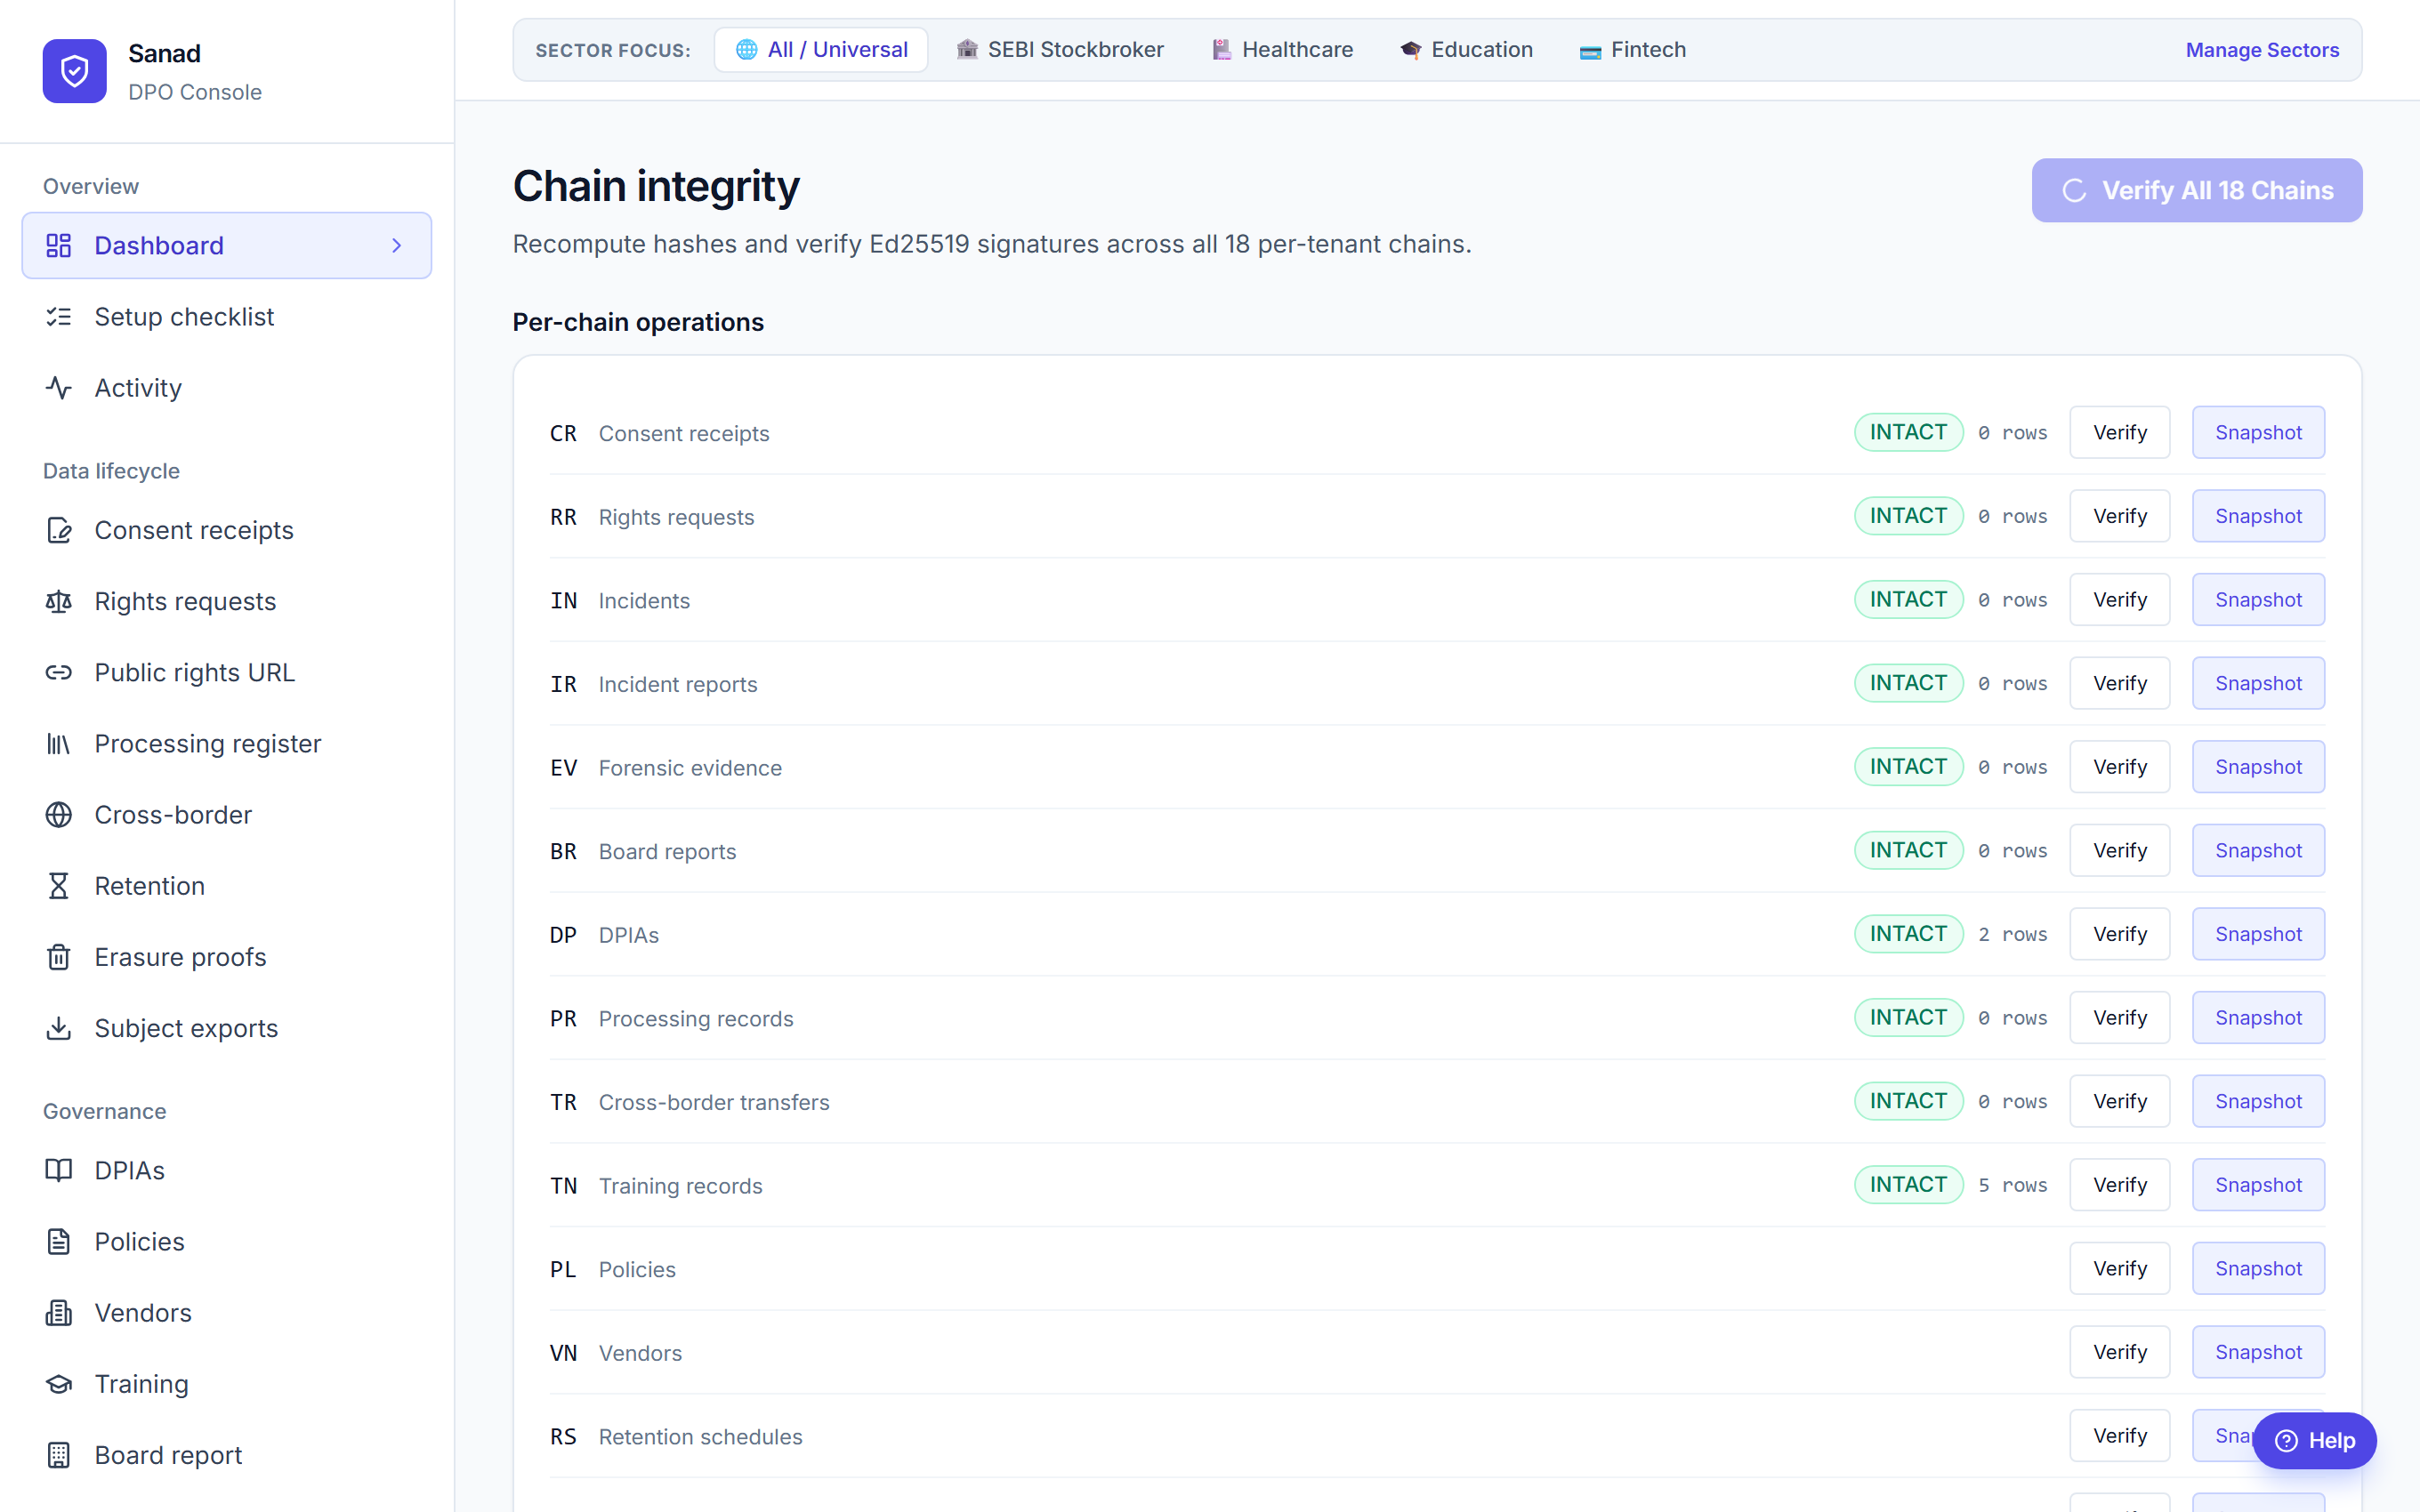
The live console — every evidence chain re-verified on demand.
Evidence, not screenshots
Every artifact — incident report, consent receipt, DPIA, policy — is cryptographically signed the moment it is recorded. When the auditor asks, you hand over proof, not a spreadsheet.
The 6-hour clock, handled
CERT-In gives you six hours to report an incident. Sanad tracks the deadline from the moment of detection, prepares the report, and dispatches it — with the timeline preserved as evidence.
From your own machines
A lightweight Windows agent collects endpoint posture, event logs and inventory automatically — hardware-attested, minimised for privacy, retained for the statutory 180 days.
Built for regulated India
One evidence platform, configured for your regulator.
SEBI-regulated entities
Stockbrokers, RIAs and intermediaries facing the Cybersecurity & Cyber Resilience Framework: audit-ready evidence for your CSCRF submissions, from asset inventory to incident timelines.
NBFCs & digital lenders
One signed record for your IT-outsourcing register, vendor risk reviews and CERT-In obligations — produced continuously, per endpoint.
State & district administrations
One dashboard showing DPDP compliance across every school, MSME, clinic and hospital in your jurisdiction — with a signed district report.
Schools, MSMEs & hospitals
Self-serve DPDP compliance sized for smaller organisations — consent, rights requests, breach response and retention, without a compliance team.
Running in an afternoon, not a quarter
Deploy the agent
Install the signed Sentinel agent on your Windows endpoints — five minutes with your license key, or push it through your existing MSI/GPO tooling.
Evidence accrues
Endpoint posture, logs, consent records and compliance artifacts are collected, signed and chained automatically. Your dashboard reflects reality, not intentions.
Hand over proof
For an audit, a regulator query or a board review: export signed reports, share verification links, and let anyone independently confirm nothing was altered.
Under the hood
The guarantees are cryptographic, not contractual — and independently verifiable.
Ed25519 signatures
Every artifact is signed with a per-tenant key; verification is public.
Hash-chained ledgers
Records link to their predecessors — edits, deletions and reordering are detectable.
Hardware attestation
Endpoint evidence is signed by the machine's TPM and verified server-side.
See your compliance posture as an auditor would.
A 30-minute walkthrough with your sector’s configuration, on live software.